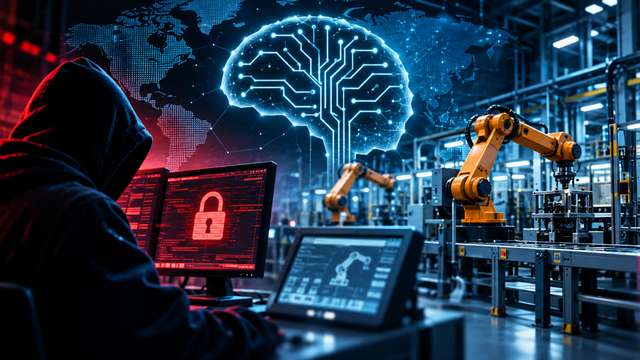
Artificial intelligence could significantly increase the scale and sophistication of cyberattacks targeting critical infrastructure over the next two years. This is the warning issued by the UK's National Cyber Security Centre (NCSC) in its latest assessment. Experts highlight the particular vulnerability of systems relying on outdated technologies and inadequate security measures. For an industrial sector increasingly dependent on automation and digital connectivity, the message is clear: cybersecurity can no longer be treated as an afterthought.
Table of content
On 3 November 2026, the UK's National Cyber Security Centre published an assessment that should concern not only IT professionals but also business leaders and those responsible for managing industrial facilities.
According to the NCSC, it is highly likely that AI-enabled malware will be used in a ransomware attack against the UK's critical national infrastructure by 2028. Such attacks typically involve criminals blocking access to systems or data and demanding payment to restore access.
This is a forecast of a potential threat, not confirmation that such an attack has already taken place. Nevertheless, the assessment from the NCSC, which operates as part of the UK's intelligence and security agency GCHQ, suggests that the risks could increase substantially in the coming years.
The greatest concern is not necessarily the emergence of entirely new attack methods, but rather the ability of AI to accelerate the identification and exploitation of existing vulnerabilities. This also has important implications for industrial infrastructure.
1. Artificial Intelligence Is Changing the Threat Landscape. China and Russia Among the Key Concerns
Until recently, launching a sophisticated cyberattack required considerable resources, specialist expertise and time. Artificial intelligence has the potential to gradually lower these barriers.
AI can automate the analysis of large volumes of information, accelerate vulnerability discovery and improve the effectiveness of certain malicious activities. In practical terms, attackers may be able to operate faster and conduct more operations simultaneously.
The NCSC warns that by 2028, countries such as China and Russia are likely to routinely use artificial intelligence to advance their geopolitical objectives in cyberspace.
British security authorities have expressed particular concern about China's capabilities, identifying the country as one of the most significant sources of potential threats to the UK's strategic systems.
However, this does not mean that every future cyberattack will be state-sponsored. Organised criminal groups may also take advantage of increasingly accessible AI capabilities, with financial gain remaining their primary motivation.
Richard Horne, Chief Executive of the NCSC, has highlighted longstanding weaknesses in technological security. The concern is that vulnerabilities which have remained unnoticed or unaddressed for years could now be identified and exploited on a much larger scale.
This is particularly significant for critical infrastructure, including energy networks, transport systems, water utilities and other services essential to the functioning of modern society.
Disruptions to such infrastructure can have consequences extending far beyond the financial losses of an individual organisation.
2. The Connected Factory: Industrial Automation Faces a New Security Challenge
Modern manufacturing facilities increasingly operate as interconnected technological environments rather than collections of independent machines.
Programmable logic controllers (PLCs), variable frequency drives (VFDs), SCADA systems, human-machine interfaces (HMIs) and industrial sensors form complex automation networks. These systems are increasingly integrated with enterprise IT infrastructure, analytics platforms and remote monitoring solutions.
This transformation offers significant benefits. Manufacturers can monitor production efficiency, analyse energy consumption, identify equipment failures earlier and improve operational performance across entire facilities.
However, greater connectivity also introduces new risks.
Every additional connection between systems requires appropriate protection. Outdated software, insecure configurations and poorly controlled remote access can all increase exposure to cyber incidents.
Importantly, attackers do not necessarily need to gain direct control of a PLC to disrupt industrial operations.
Losing access to production management systems, technical documentation or essential operational data may be enough to cause serious difficulties. In some cases, production may need to be temporarily suspended until the safety and integrity of affected systems can be verified.
Older industrial installations present a particular challenge.
Many manufacturing facilities still rely on equipment that has been operating successfully for fifteen, twenty or even thirty years. Such machinery may remain mechanically reliable and perfectly capable of performing its intended functions.
The problem arises when its control systems were never designed to withstand today's cybersecurity threats.
Modernising these installations is not always straightforward. Replacing a controller may require software modifications, compatibility assessments and, in some cases, substantial changes to the existing automation architecture.
For this reason, industrial cybersecurity must become a shared responsibility involving IT departments, automation engineers and maintenance professionals.
Protecting office computers is simply not enough if the systems responsible for operating production equipment remain inadequately secured.
3. Industrial Maintenance in the Age of Cyber Threats: Is Manufacturing Prepared?
The NCSC's assessment raises an important question for industrial businesses: can they maintain operations if part of their digital infrastructure suddenly becomes unavailable?
For manufacturing companies, the answer depends on several factors.
The starting point is a clear understanding of the existing infrastructure. Businesses need to know which devices are operating within their facilities, which systems are connected to networks, what software they use and whether their manufacturers still provide technical support.
Other essential measures include separating corporate IT networks from operational technology (OT) environments, controlling remote access, maintaining reliable configuration backups and regularly assessing available security updates.
In industrial environments, however, software updates must be carefully planned to account for compatibility, operational safety and production continuity.
The availability of replacement components is another important consideration.
If a cyber incident results in the need to replace a controller, communication module or another industrial device, the time required to source a suitable replacement may directly affect how quickly production can resume.
This is where the expertise of companies such as Automation Trader, which specialises in supplying industrial automation components, becomes particularly relevant.
Access to hard-to-find parts, extensive knowledge of the industrial components market and the ability to identify suitable replacement solutions can help businesses minimise downtime.
Of course, replacing a device does not eliminate the underlying causes of a cyberattack, nor does it substitute for effective cybersecurity measures.
It does, however, demonstrate that industrial resilience requires a comprehensive approach. Cybersecurity, equipment reliability, component availability and emergency response procedures must all be considered together.
It is also worth remembering that artificial intelligence is not exclusively a tool for attackers.
AI-powered technologies can support threat detection, identify unusual system behaviour and help security teams respond more quickly to emerging incidents.
In practice, this creates a technological race in which industrial companies must continuously strengthen their defences while expanding their digital capabilities.
The British warning does not mean that European factories will inevitably be paralysed by cyberattacks in 2028. It does, however, indicate that the potential use of AI against critical infrastructure represents a sufficiently serious threat to warrant action today.
For manufacturers, the conclusion is straightforward: modern industrial automation must go hand in hand with cybersecurity and operational resilience.
After all, the reliability of a modern factory is determined not only by the quality of its machinery, but also by the resilience of the entire technological environment that keeps that machinery running.